TL;DR
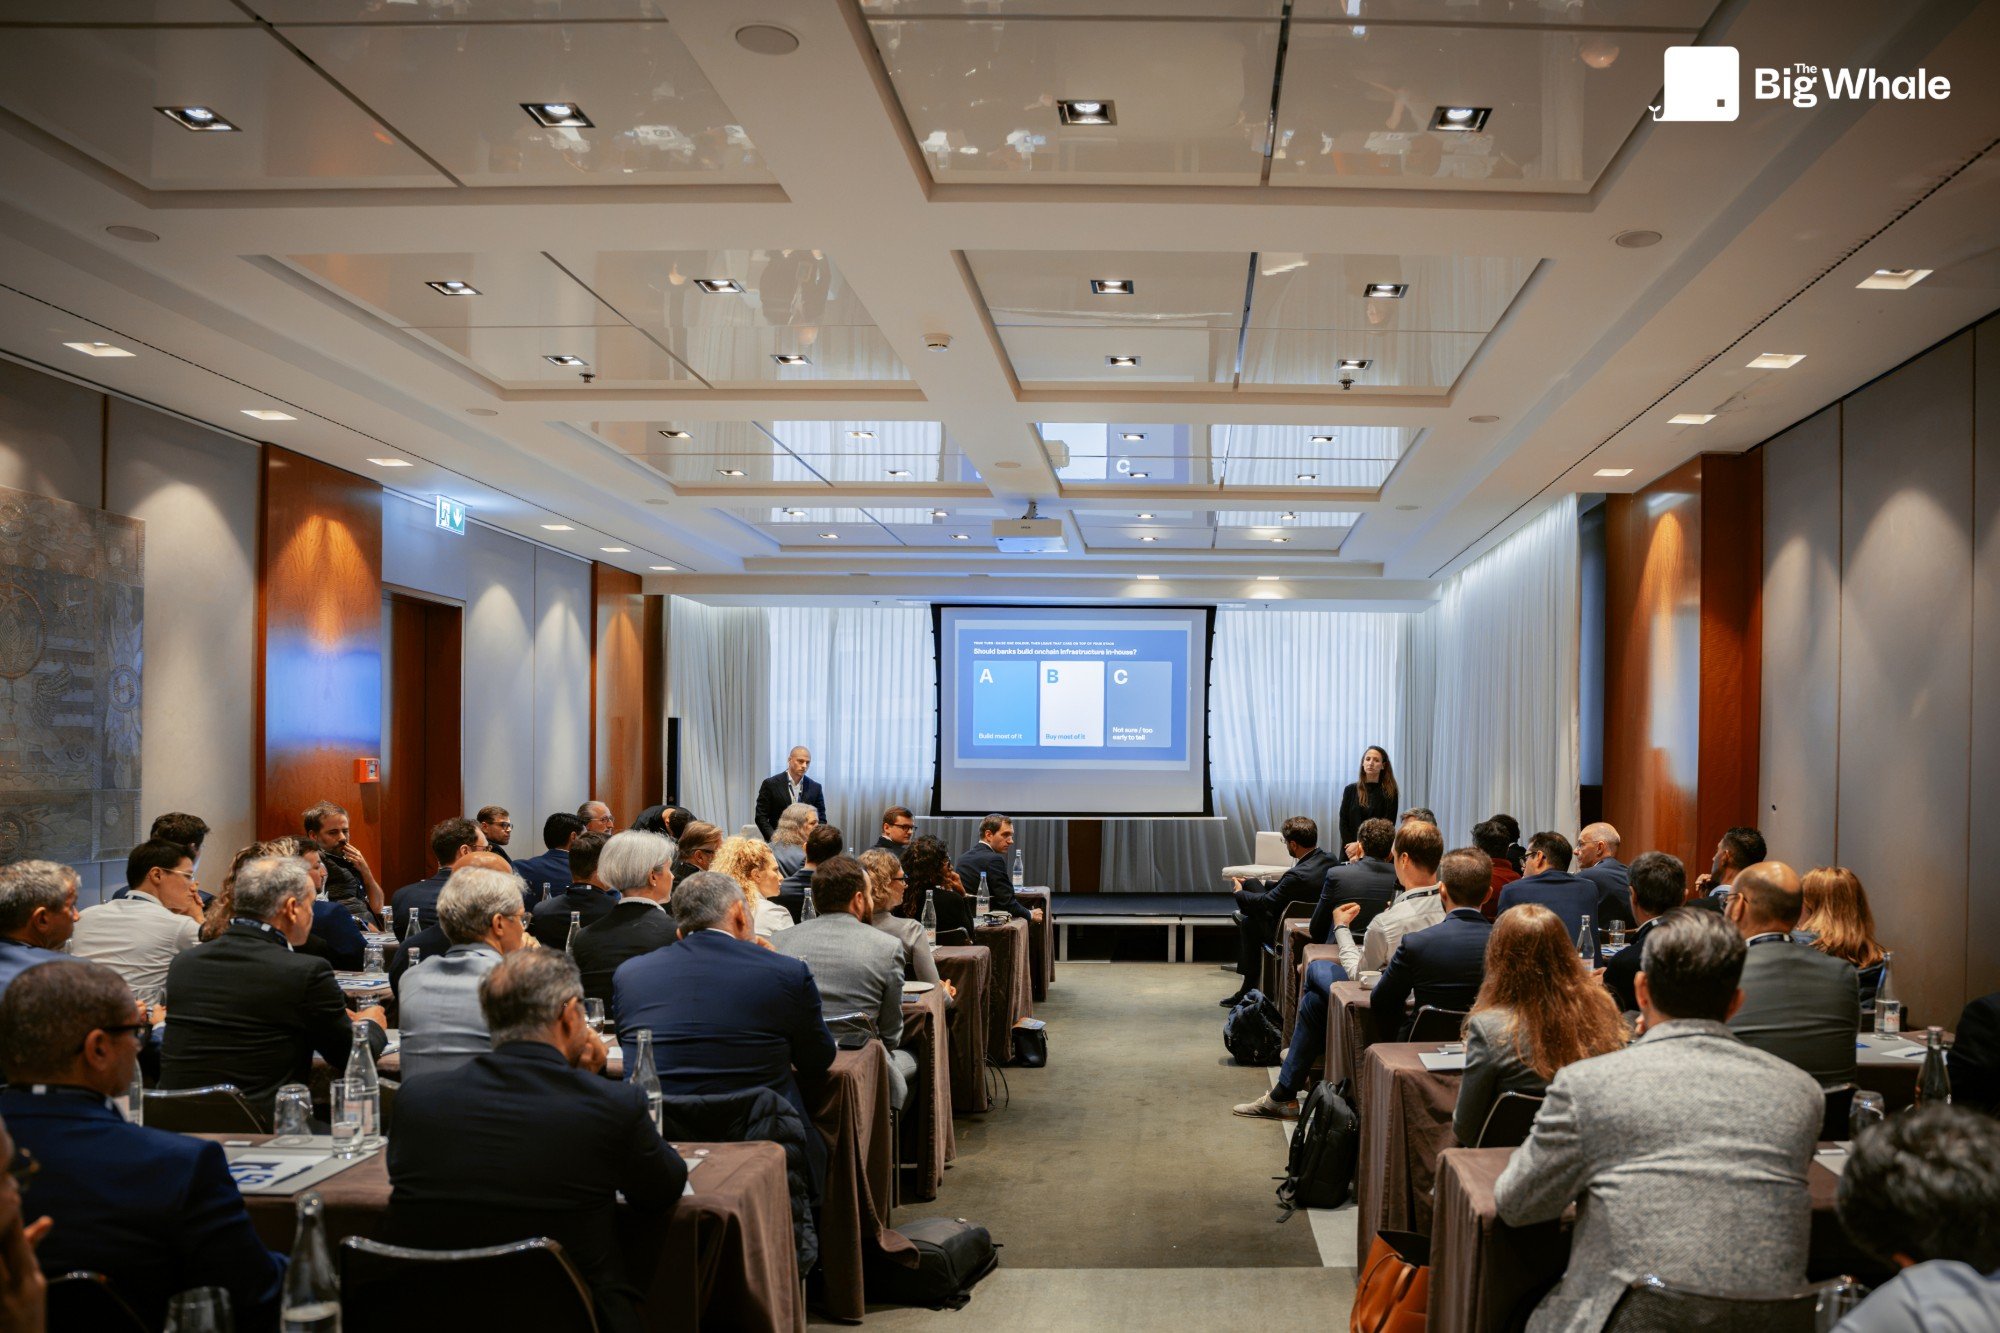
- Asked whether banks should build onchain infrastructure in-house, about 70% of the room answered buy most of it, 20% build most of it and 10% not sure. In practice, participants described a mix: operate the critical parts, buy specialised components and connect them.
- The layer almost everyone wants to own is the orchestration layer between onchain providers and the bank's systems, to avoid lock-in and to swap or add vendors over time.
- Resilience came up repeatedly: after the $6 billion Binance hack, participants advised planning a second and third provider for each component, and expect regulators to ask for it.
- Operations are where banks struggle most: settlement with liquidity providers has no blueprint, and teams need new skills, separation of functions and a step-by-step rollout.
- The choice of blockchain often decides how much a bank can build alone: a single permissioned chain can be run in-house, while connecting to several public chains usually requires outside help.
- For Clarisse Hagège, institutions buying infrastructure are buying control, which means API-first, modular and on-premise options, as regulators become more prescriptive on where data runs and who controls it.
Speakers
Should Banks Build Onchain Infrastructure In-House, or Is That a Battle They've Already Lost?
- Clarisse Hagège, Co-CEO at Dfns
The workshop was held under the Chatham House Rule: statements by participants are reported without names or affiliations.
Where the budget goes
Clarisse Hagège, a former banker who founded Dfns six years ago, opened by describing how the company now presents itself: as core banking for digital assets, because banks do not want to become crypto firms, they want to remain banks that can handle digital assets. Dfns works with more than 300 clients, from payment providers such as Stripe and MoonPay to banks such as Barclays and JPMorgan and market infrastructures such as Nasdaq. According to Clarisse Hagège, most projects now start with the cash leg and are led by transaction banking, while capital markets use cases are moving from proofs of concept to production.
The moderator described the stack banks need, from key management and hardware up to client channels, and how their spending on it is split:
- Most of the budget goes to internal staff: product, engineering and compliance
- 15 to 25% goes to external staff such as lawyers, auditors and implementers
- 15 to 20% goes to technology providers
According to the moderator, this does not mean banks build most of the solution themselves, only that the internal part costs them the most.
Build most, buy most, or operate most
The room voted on whether banks should build onchain infrastructure in-house: about 20% answered build most of it, 70% buy most of it and 10% not sure. Clarisse Hagège focused the discussion on the words most of it, and on which part banks should own, since many jurisdictions now treat this infrastructure as strategic and as a security matter.
The participants who described their own projects rarely chose one side:
- The head of a French banking group's digital asset subsidiary said the group chose to operate most of the stack rather than build it, owning the core of custody, the HSMs and key servers, and connecting several specialised vendors through an in-house, event-driven orchestrator. The subsidiary was built on the side, with limited links to the group's core banking system, so it can plug into several banking apps
- A payment service provider took the opposite route and integrated digital assets directly into its existing microservices, so clients use the same product whether they hold euros or digital euros, while relying on an outside service for blockchain transactions
- A large bank chose a white-label platform integrated into its core, because tax, reporting, settlement and reconciliation would otherwise have to be rebuilt from scratch
Clarisse Hagège compared the standalone model to those of Forge or Kinexys, and noted a common fear among clients: that connecting digital assets to the legacy core could disrupt the bank's day-to-day cash management.
Own the orchestration layer, plan for several vendors
A participant in charge of digitalisation at a bank said the size of the institution shapes the answer, but that every bank should own the abstraction layer between its onchain stack and its internal systems, even when buying a fully integrated product. Without it, the bank depends on a single vendor and cannot build redundancy for each component, from custody to financial crime screening. According to this participant, banks picking a single provider today will find that one is not enough.
A participant from a market infrastructure went further: after $6 billion was taken from Binance the previous week, nobody should put all their eggs in one basket, and every component should have a second, third and fourth option. This participant expects regulators to ask for the same resilience as in other asset classes. Asked whether owning the whole infrastructure would make a bank safer against cyberattacks, nobody in the room said yes.
A participant from a global payments network expects banks to want choices: specialised digital asset providers, or their existing core banking vendors adding digital asset features. This participant encouraged the room to look at the technology behind each provider and favoured open source to avoid technical debt. Clarisse Hagège said Dfns open-sourced its multiparty computation cryptography early for the same reason.
Why some asset managers built their own
Clarisse Hagège expected asset managers to rely on their custodians and transfer agents, and has instead seen large firms build their own digital asset stack, partly to control distribution. A participant from a large asset manager said the firm built its custody infrastructure from scratch years ago, because no provider met its criteria at the time and because of its fiduciary duty to clients. The firm custodies Bitcoin, Ethereum and Solana for institutions, but not tokenized assets yet, since it is not clear which models will last. According to this participant, building required a capital commitment from the top and comes with limits on what the firm can offer.
Operations are the hard part
The head of the bank subsidiary described the operating model for offering crypto to retail clients inside existing banking apps:
- Trade execution resembles capital markets, with FIX connections and confirmations from venues
- Settlement with liquidity providers has no blueprint: each provider is different, and the process needs constant tuning and contingency plans, for example when SEPA is down
- IT operations are run by the group's existing teams, with limited knowledge of the key infrastructure as a security measure, and with a strict separation of functions
- The service required a French PSAN registration, a full IT security audit and a new product committee, and started with all flows blocked before opening them gradually
A participant who has run a tokenized money market fund for nine months built an observe-only dashboard so that operations and other teams could follow flows across wallets and providers, and advised against automating everything at once.
The blockchain decides how much you can build alone
For Clarisse Hagège, most conversations with financial institutions start with the choice of blockchain, often a permissioned one, which a bank can run itself. The build or buy decision changes when the bank plans to connect to public chains: managing several networks, keeping up with their features and adding privacy layers becomes technology that is not core to the bank, and that is where it needs help.
Participants stressed the network effect:
- Choosing a chain takes large institutions about six months, and by then the market has moved
- Payments and stablecoins may converge on a few networks with critical mass, and investment products need the same
- One participant said banks spent years treating blockchain as a foundational technology to pick once, and that walled gardens do not work without critical mass
A participant from an infrastructure provider compared the current phase to the internet before HTTP, when separate networks coexisted, and expects a multi-chain, multi-asset world. This participant argued that stitching providers together through middleware only works if security and governance are designed in from the start, and proposed an account-centric architecture, where a wallet acts as the digital twin of a bank, securities or treasury account.
Conclusion
As Clarisse Hagège noted, every participant who argued for building in-house also mentioned a part they had bought. The banks that spoke keep control of custody keys and of the layer that connects their providers, buy specialised components and plan for several vendors from the start. Clarisse Hagège summed up what institutions look for as control: APIs to integrate with legacy systems, a choice between HSM, MPC and cold storage depending on the use case, and on-premise deployment where regulators require it. Clarisse Hagège expects supervisors under MiCA to become more prescriptive about where data runs and who controls it, and wants choices made today to stay compatible as banks add chains and assets.